Written by
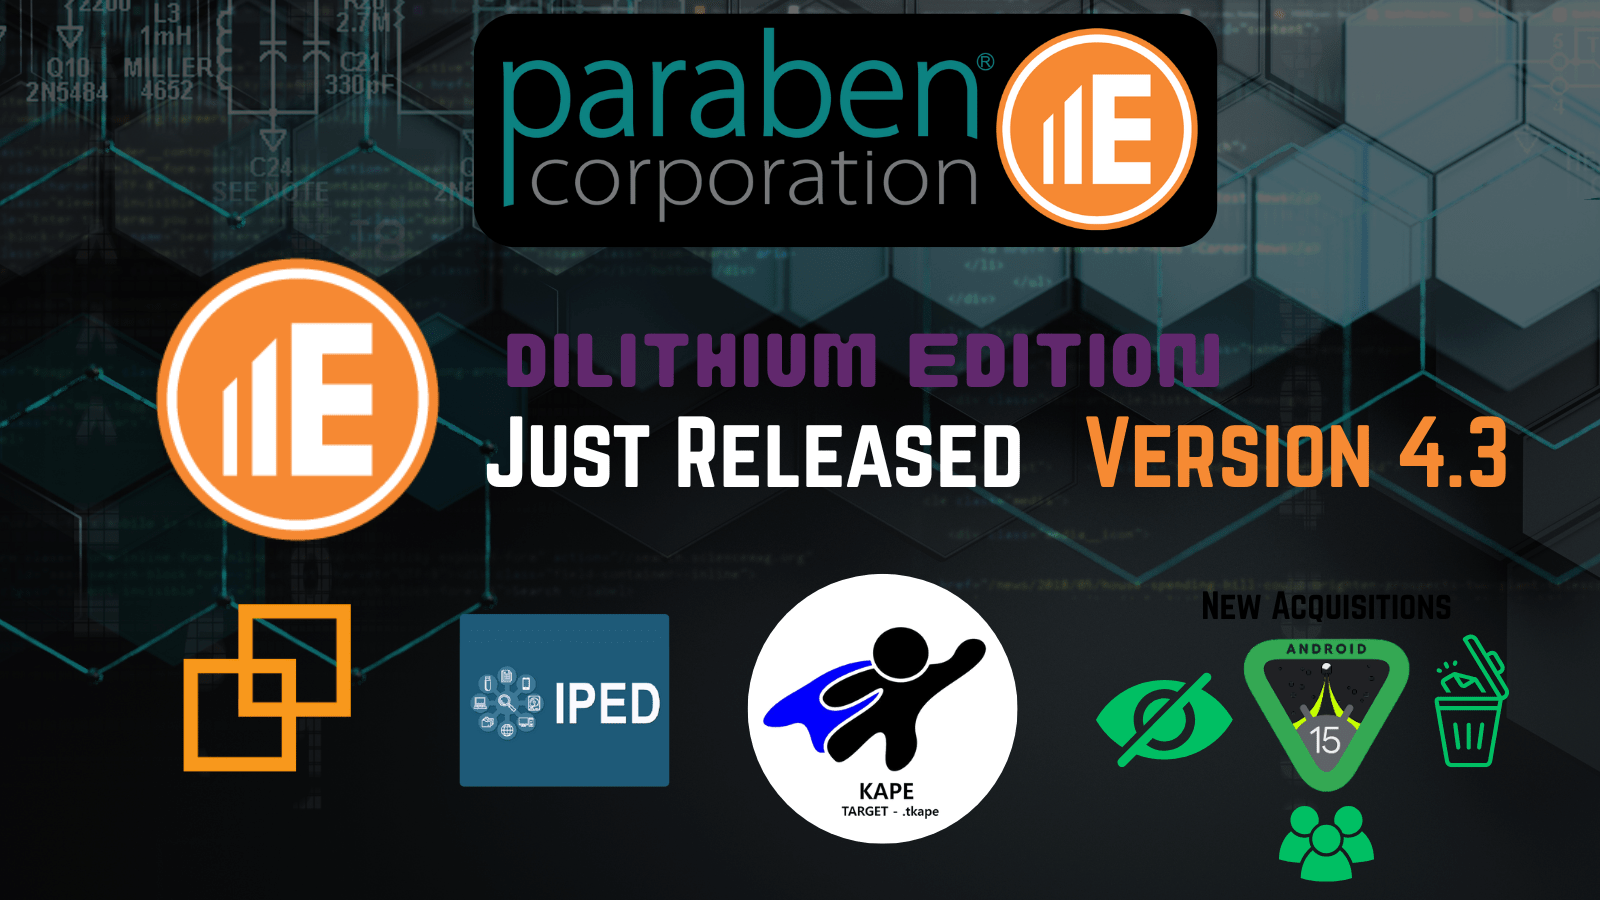
Paraben Corporation, a global leader in digital forensics solutions, today announced significant updates to its flagship E3 Forensic Platform, further empowering investigators with enhanced data processing and analysis features. The latest releases focus on streamlining data import workflows and providing deeper insights into Android device data.
“This latest innovative release underscores our unwavering commitment to the DFIR community,” affirmed Amber Schroader, CEO and Founder of Paraben. “We remain dedicated to providing accessible DFIR capabilities to organizations of all sizes while steadfastly supporting the crucial role of digital evidence in the justice system.”
A key enhancement includes an extended Logs & Artifacts Import Wizard. Investigators can now seamlessly import even more diverse datasets, including:
- Archives containing CSV files generated by KAPE (Kroll Artifact Parser and Extractor) tool modules, allowing for efficient integration of targeted artifact analysis results.
- Output folders from IPED (Image Processing for Evidence Discovery) Digital Forensic Tool, simplifying the incorporation of disk image processing findings into the E3 platform.
These expanded import options provide investigators with greater flexibility and efficiency in consolidating critical evidence from various forensic tools within the unified E3 environment.
The latest E3 Forensic releases deliver enhanced capabilities for Android device analysis:
- Investigators can now easily view a comprehensive list of applications installed within an Android Private Space, providing crucial visibility into potentially hidden or segregated app usage.
- The Installed Application List grid now includes valuable information on whether an application has been removed from an Android device, aiding in the reconstruction of user activity and identifying potential tampering.
- Acquisition of multiple user accounts with Android devices.
These Android-focused updates equip forensic examiners with more granular control and deeper understanding of mobile device data, which is increasingly vital in modern investigations.
These new features are part of the continuous evolution of the E3 Forensic Platform.
To enhance cross platform compatibility new export features to allow compatibility with Relativity have been added.
- Export of file system data to Load files.
- Export of Smartphone data to load files.
- Export of iOS and Android messaging data to RSMF format.
Paraben Corporation’s ongoing commitment to providing cutting-edge solutions for the digital forensics community at prices that are accessible to any budget.
Stay updated with the latest advancements in digital forensics by visiting Paraben Corporation and following them for updates.
Forensic-Impact Articles
Why Digital Evidence Needs a Behavioral Read, Not Just a Technical One
Oct 20, 2026
Guest Blogger: Kevin Schell No matter what your line of work, you’ve sat across from someone and thought you could read them, something in their eyes, the way they moved. It’s a gut thing. You can’t say whether it’s right, and when researchers have tested it, as in...
Blockchain Forensics Is Only the Beginning
Oct 13, 2026
Bridging On-Chain Analysis, OSINT, and Digital Evidence Guest Blogger: Matthew Stern Cryptocurrency investigations are often described as the virtual equivalent of “following the money.” Public blockchains such as Bitcoin and Ethereum give investigators an unusual...
Building an Autonomous Network Honeypot & Deception Matrix
Oct 6, 2026
Guest Blogger: Fuzuyise Khoza 1. INTRODUCTION TO LOCAL NETWORK DECEPTIONTraditional network defense mechanisms operate reactively, relying on alert signatures after a system breach has occurred. In low-resource enterprise infrastructures or high-risk operational...