Forensic Impact
Insights for digital investigators: analysis, casework guidance and lessons from the forensic front line.
Avoiding AI Slop: A Digital Investigator’s Checklist for Quality Tools
Artificial intelligence can help digital forensic investigators, and private investigators manage difficult workloads. It can prioritize images, make audio searchable, and surface communications that deserve closer examination. But an “AI-powered” label does not establish forensic-grade reliability.
Read article →All articles
Why Digital Evidence Needs a Behavioral Read, Not Just a Technical One
Guest Blogger: Kevin Schell No matter what your line of work, you’ve sat across from someone and thought you could read them, something in their eyes, the way they moved. It’s a gut thing. You can’t say whether it’s right, and when researchers have tested it, as in the Bond and DePaulo meta-analysis
Blockchain Forensics Is Only the Beginning
Bridging On-Chain Analysis, OSINT, and Digital Evidence Guest Blogger: Matthew Stern Cryptocurrency investigations are often described as the virtual equivalent of “following the money.” Public blockchains such as Bitcoin and Ethereum give investigators an unusual advantage: a transaction history th
Building an Autonomous Network Honeypot & Deception Matrix
Guest Blogger: Fuzuyise Khoza 1. INTRODUCTION TO LOCAL NETWORK DECEPTIONTraditional network defense mechanisms operate reactively, relying on alert signatures after a system breach has occurred. In low-resource enterprise infrastructures or high-risk operational perimeters, defenders must deploy pro
How Government Buyers Can Verify Digital Forensics Vendor Provenance: A Practical Guide
When government agencies buy digital forensics tools, they aren’t just buying software. They’re investing in the integrity of evidence that can affect people’s liberty, national security and public trust. Recent federal attention to supply chain and foreign-adversary risk shows that checking a vendo
The Four Foundation Questions of Digital Forensics
In digital forensics, technology moves at lightning speed and lately at GPU speed as well. Apps, encrypted mobile operating systems, cloud artifacts, and complex IoT devices change almost daily. Yet, despite this constant evolution, the core foundation of legally defensible digital forensic science
Before Direct NAND Acquisition: Diagnosing an Undetectable Monolithic SD Card
Guest Blogger: Yevgeniy Kapishon | Aesonlabs Data Recovery Undetectable Is a Symptom, Not a Diagnosis When an SD card is not detected by a computer, reader or recovery system, the failure is often attributed immediately to the controller or NAND flash memory. With monolithic media, that assumption c
How OSINT Supports Compliance and Due Diligence
Guest Blogger: Issam Hanbali Open-source intelligence, commonly known as OSINT, is often associated with cybersecurity investigations, digital forensics, threat actor research, and online reconnaissance. However, OSINT also plays an increasingly important role in compliance and due diligence. For fi
No Photons, No Alibi
A Conservation-of-Trace Framework for Authenticating Imagery in the Age of Generative AIGuest Blogger: Khaled S. Al Sannat Generative models have dissolved the oldest working assumption of visual evidence: that a photograph is, by default, a witness. The reflex of the field has been to ask a binary
Unmasking the Synthetic: Using Metadata to Spot AI-Generated Images
Most images now feel like they have the touch of AI, where they feel too perfect. Sometimes the image looks clean, the lighting checks out, and the subject seems real. It is time to start doubting the content and do a deeper dive. I’ve been looking at image files for a long time, and one
Mapping Threat Patterns Using Publicly Available Data
Guest Blogger: Ruqaya Osman Cybersecurity teams have long operated in two distinct lanes: those who investigate incidents after they occur, and those who gather intelligence to anticipate future threats. Digital Forensics and Incident Response (DFIR) practitioners focus on what happened inside the n
Transition from Traditional Forensic Science to Digital Forensics: Challenges, Lessons, and Opportunities
Guest Blogger: Vaishnavi M.A. My journey into forensic science began with a desire to pursue something unique and intellectually stimulating. I have always been curious by nature and enjoyed solving problems, which led me to choose forensic science as my field of study. During my academic journey, I
Investigative Perspective Claude Mythos AI
Guest Blogger: Sheetal Kumari At: MAD Forensics With the new age of AI, which has already arrived , showing continuous growth has introduced the world to a technology that is making advancements towards making human life easier yet also creating new dilemmas with unintended consequences . To prevent
The Recipe for the American Dream: Lessons from a 3 AM Workbench
I was born into a family of immigrants who followed their own dream to the United States to build a business from scratch. When I was a little girl, my mom and I lived with her parents after her divorce. That cozy house was the backdrop for the first years of my life, a time
Investigating Fileless Malware Through Volatile Memory Forensics: Building an Open-Source DFIR Workflow
Guest Blogger: Anas Zahid Fileless malware has become one of the most challenging threats facing modern defenders. Unlike traditional malware, fileless attacks often operate entirely within memory, leveraging trusted operating system components such as PowerShell, Windows Management Instrumentation
Decoding Financial Fraud: Tools and Methodology
Guest Blogger: Vladislav Hamppu Many people think that online investigation is just a Google search. In reality, it’s about working with digital footprints and automation. Using my recent case as an example, here is how it works in practice: First Environment Setup I don’t work from a standard Windo
Behind the Scenes of ClickFix: Blockchain-Based Dead Drop C2 Resolver
Guest Blogger: Manasi Joshi What if a malware’s C2 infrastructure wasn’t hardcoded, but resolved dynamically from a blockchain? I was recently analysing a ClickFix campaign. While analysing, I expected the usual, hardcoded domains, maybe some layered obfuscation. That’s not what showed up. There was n
Understanding the Risks of AI in Investigations
When data integrity is everything, hooking an AI tool directly into your investigation workflow is a major security gamble especially when dealing with sensitive evidence, login credentials, or PII. As AI becomes a standard feature in forensic tools and other digital investigation tools, we can’t ju
OSINT and Infidelity with Private Investigations
Guest Blogger: Taylor Weddington Digital footprints are nearly impossible to erase; the art of uncovering infidelity has undergone a profound transformation in 2026. Open-Source Intelligence (OSINT) resources such as social media platforms, public records, online databases, forums, photo metadata, a
Why do tools show different results?
Since I started working in the DFIR space many years ago I always remembered the rule of two tools. That rule, although stated, is not always followed by every examiner. With the rising costs of DFIR tools many organizations have only funded one tool for their teams, and they rely on the community t
Inside Malicious Office Documents
Guest Blogger: Luca Garofalo Today whether it is at work, in school or any other context we receive documents. They are very usefull they allow us to keep informations in a more organized way thanks to tables, images and text formatting. However some documents can contain malicious code that in most
If Digital Evidence Could Lie: How Machines Create False Truths
Guest Blogger: Shatakshi Khadke “In the courtroom, machine-generated timelines often speak louder than human doubt.” Digital evidence is presented into court with an invisible badge of authority. A timeline is extracted by a tool, a log generated by a system, or a visualization produced by software
Invisible Intelligence: Navigating the Risks of Unsanctioned AI in Digital Investigations
Shadow AI occurs when employees deploy artificial intelligence applications or services without the explicit knowledge, approval, or oversight of IT and security departments. Similar to using a personal cloud storage account for corporate files, this practice creates significant “blind spots” by blu
AI Doesn’t Need a Trust Score
Guest Blogger: Stephen Coston The views expressed are my own and do not represent those of my employer or any affiliated organization.Courts Don’t Regulate Tools. They Regulate Testimony. Every few months, the same question resurfaces in legal and forensic circles: “How much should we trust AI?” It
Stop Fearing the Algorithm: Why AI Only Threatens Expertise Without Outcomes
Guest Blogger: Donald Wochna I am somewhat bemused by the hyper-sensitivity that the market seems to have for the impact of AI on the practice of law. For example, last week, in response to Anthropic’s Claude announcing a plug in for attorneys, competing Legal service companies’ valuation plummeted
Oculus Data Artifacts
In the rapidly evolving landscape of digital forensics, the objects of our investigations often move faster than our tools. While the industry is currently focused on the latest “Mixed Reality” headsets, a significant volume of digital evidence still resides on legacy devices. With the recent announ
Democratizing Threat Intelligence: SME Cyber Defense Strategy Framework.
Guest Blogger: Junaid Arshad Malik Small and Medium Enterprises (SMEs) and Small Office/Home Office (SOHO) networks are in a very precarious state in the existing digital ecosystem. These networks have ceased to be mere small fish to cybercriminals; they are soft jumps, convenient points of entry to
TCP Traces: How Malicious Traffic Disrupts the Linux Network Stack
Guest Blogger: Fred Peña UrbinaMalicious traffic rarely looks “broken” at a glance, but it often leaves subtle inconsistencies in how the TCP/IP stack behaves. These inconsistencies timing irregularities, retransmission bursts, or unexpected window advertisements, become valuable clues during early
Memory Forensics Beyond the Endpoint: Volatile Evidence in Modern Cloud and Edge Environments
Guest Blogger: Aditya Srikar KonduriWhen learning memory forensics, many guides show you how to snapshot RAM from desktops and extract volatile artifacts from familiar endpoints. But step into the world of modern cloud deployments, and “memory acquisition” takes on new, urgent complexity. The tradit
Mastering the Essential Skills of a Digital Investigator
In our increasingly interconnected world, the need for skilled digital investigators has never been greater. From cybercrime to corporate espionage, these digital detectives play a crucial role in uncovering truth and ensuring justice. But what exactly makes a good digital investigator, and how can
The First Documented Fully Autonomous AI-Driven Cyber-Espionage Campaign
Anthropic released a paper late last week which describes what may be the first known case of a nearly fully autonomous AI-conducted cyber-espionage operation, attributed to a Chinese state-sponsored threat group dubbed GTG-10002. According to the paper, this incident “represents a fundamental shift
Preserving the Past through Digital Forensics
Data can be created, altered, or destroyed in the blink of an eye. This fact gives rise to the single most important principle in digital forensics, a principle so fundamental it is the first thing you are taught when entering the field. Preserve the Data The moment an investigator approaches a comp
DFIR: The Importance of Understanding Types of Evidence When Making Decisions
Guest Blogger: Anthony DourraWhen learning DFIR skills, there are many sources that teach how to use tools to collect evidence and how to maintain a chain of custody to ensure the integrity of evidence. And there are many sources that teach the analysis of evidence. But in textbooks and conceptual v
Why OSINT + DFIR is the Ultimate Power Couple
We are living in a hyper-connected, threat-saturated digital landscape, incident responders and forensic investigators can no longer afford to work in silos where there is no information sharing. As we see more of our individual industries come together to get part of the larger cyber picture one of
The Silent Witness in the Sky: A Deep Dive into Drone Forensics for Criminal Investigations
Guest Blogger: Ankit BhardwajThe proliferation of drones, once a novelty, has ushered in a new era across industries, from logistics and agriculture to cinematography and surveillance. However, this technological leap has a darker side: the increasing exploitation of Unmanned Aerial Vehicles (UAVs)
How to Successfully Incorporate AI into Your Business: Best Practices, Challenges, and Real Benefits
Guest Blogger: Lance Cody-ValdezIf you’re running a business today, artificial intelligence (AI) is no longer a futuristic option, it’s a tactical decision. From automating routine tasks to revealing strategic insights, AI has become a powerful tool that can reshape how companies operate. But it’s
Data Breaches Explained: Biggest Threats, Causes, How to Check, Protect & Fix Your Data
Guest Blogger: Shatabdi MalikIn today’s hyper-connected world, data breaches aren’t rare headlines anymore, they’re daily reality. Over the past year alone, we’ve seen record-shattering leaks that have compromised millions, and in some shocking cases, billions, of sensitive records worldwide. One
Unmasking the Digital Penman: An Introduction to Forensic Linguistics
Guest Blogger: Sarah Carlson, Forensic LinguistIn the world of digital forensics, piecing together digital breadcrumbs is critical for understanding events, identifying perpetrators, and building cases. But what if the evidence wasn’t a timestamp or an IP address, but the very words used in an email
Securing Digital Evidence: Best Practices for Small Business Owners
Guest Blogger: Lance Cody-ValdezHandling digital evidence isn’t reserved for massive corporations or courtrooms. Small businesses find themselves managing it more often than they think, through internal audits, security incidents, or customer disputes. But the evidence itself is only part of the stor
The Unfair Standard: Why We Expect AI to Be Perfect When We’re Not
There was a reference to a forensic expert who was in a courtroom, attempting to make a case for a new method they’d come up with to figure out a vehicle’s speed from dashcam footage. The case was heartbreaking, a father on a homemade motorcycle, killed by a drunk driver barreling down the road at 10
How Digital Forensics Fits into Cybersecurity
Digital forensics is an essential pillar of modern cybersecurity. As cyber threats grow in complexity and frequency, organizations rely on digital forensics to investigate, respond to, and learn from security incidents. This specialized field not only uncovers the details of cyber-attacks but also s
Detection, Analysis, and Interpretation of Fake Base Stations (IMSI Catchers) in Mobile Forensics
Guest Blogger: Haydar Yener ArıcıA crime does not always begin with the sound of a trigger; sometimes it starts with a darkened screen, the silent relocation of a SIM card, or a device unknowingly connecting to the wrong party. Fake base stations (IMSI Catchers/Stingrays) are among the leading threa
From Solitary Sleuth to Connected Pro: Networking for Introverted Digital Investigators
With June kicking off the event season, this blog topic came to mind. As a natural introvert, events always come with a bit of anxiety for me, so hopefully, these tips will help others too. As I delved into this topic, I found some fantastic resources. Debbie Gardner and Jessica Hyde shared great ne
Speaking Their Language: How Investigators Can Connect with Anyone
Guest Blogger: Lance Cody-ValdezIn today’s hyper-digital world, the value that digitally focused professionals and investigators bring to an organization is undeniable. From system upgrades to data security, infrastructure management to agile development, forensic imaging, the scope of their respons
iOS Hidden & Locked Apps
iOS updates are always a whirlwind of new features, and iOS 18 is no exception. While the headline-grabbing changes often focus on revamped interfaces and flashy tools, there’s a quieter revolution happening beneath the surface: the ability to manage and even hide apps in ways we haven’t seen before
Building Hypervisor-Grade AI Isolation and Forensics on Oracle Cloud Infrastructure
Guest Blogger: Stephanie HonoreAs AI workloads become strategic assets and high-value targets, cloud practitioners must implement robust isolation, monitoring, and forensic capabilities. Here’s how to architect, deploy, and monitor AI workloads on OCI using state-of-the-art security and forensics pr
OSINT Tool Perspective
Guest Blogger: Nathan BlockOSINT, or Open-Source Intelligence, is a methodological process involving the systematic collection, evaluation, and analysis of publicly accessible information from diverse sources to produce actionable intelligence. Its primary purpose is to generate relevant and context
Windows Log Analysis: From Raw Data to Forensic Insights
Guest Blogger: Vamsi Krishna Chinta Understanding raw log locations in Windows and efficiently extracting and structuring them is crucial for forensic investigations and incident response. Eric Zimmerman’s tools provide a powerful way to process these logs, making them more accessible and actionabl
Essential Tools Every Small Consulting Business Needs to Grow
Guest Blogger: Lance Cody-Valdez Editor: Amber SchroaderIn the fast-moving world of small business, digital tools are no longer a luxury, they’re a survival kit. This is even more important when you rely on technology for your small business to make money. But let’s be real: the internet is ove
The Evolution of OSINT: Introducing the New Plessas Digital Knowledge Base
In the ever-evolving landscape of digital forensics and investigation, access to quality OSINT (Open Source Intelligence) tools and methodologies has never been more crucial. Today, we’re excited to share a groundbreaking development in the OSINT community that aligns perfectly with our mission at P
How Data Analytics Is Changing the Way Businesses Operate
Guest Blogger: Lance Cody-ValdezData analytics plays a key role in shaping effective strategies within business operations. If you are operating your own business for digital forensic or cyber consulting, the integration of data-focused approaches allows you to improve decisions and boost efficiency
What is threat hunting?
Guest Blogger: Nizar B.Threat hunting is a proactive approach to cybersecurity where security researchers actively search for signs of malicious activity within an organization’s network and systems. Unlike traditional security measures that rely on reactive alerts, threat hunting involves going bey
2024 Digital Forensic Review
As I look back at 2024, there were a lot of shifts in the digital forensic space and the overall digital information arena. It is always hard to stay on top of things that change as often as these areas do, so I really appreciate all the valuable contributions from guest bloggers this last year.
Drone Forensics: Navigating the new frontier of digital evidence
Guest Blogger: Ria GhoshDrones are rapidly becoming part of our daily landscape, used in industries from agriculture to media, and even for personal leisure. As they grow in popularity, they also pose unique challenges for forensic investigators. Drone forensics is an emerging field dedicated to the
Cryptocurrency and the Dark Web: A Guide to Investigation
Guest Blogger: Silvia GonzalezThe emergence of cryptocurrency has revolutionized the financial landscape, introducing new investment opportunities and challenges. While digital assets like Bitcoin and Ethereum offer a decentralized and secure means of transaction, they have also become a haven for c
From First Responder to Incident Responder
Digital Privacy: A Computer Crimes Investigator Perspective
Guest Blogger: Jacob SipeIn my years of service with the military, I had the unique opportunity to dive into computer forensics and digital privacy. As a computer forensics analyst and Computer Crime Investigator, I developed my skills in understanding and dissecting digital devices and uncovering t
Become a Digital Forensics Entrepreneur: A Quick Guide
Building a business is like raising a child. You invest time, energy, and love into its growth. After 25 years with Paraben, I’m filled with pride and gratitude to see how far it has come. It’s a testament to the hard work and dedication of our team, and I’m thrilled by the positive impact Paraben
Critical Infrastructure and IoT Survivability
Guest Blogger: Luther “Chip” (Chip) HarrisThis content represents a particular viewpoint and may not reflect the views of all individualsHere is what is going to affect the current landscape that we deal with in the Integrating the Internet of Things (IoT) into critical infrastructure in cities can
Memory Forensics Tools Overview
Guest Blogger: Kokab RasoolMemory forensics is becoming more essential in incident response and threat analysis as new threats and sophistication arise in the changing cybersecurity landscape. Memory forensics, as opposed to traditional approaches that rely on hard drive analysis, explores volatile
Unmasking Fake Emails: Essential Techniques for Email Analysis
Guest Blogger: Shatabdi MalikIn today’s digital age, emails are a prime target for scammers and cybercriminals. Identifying fake emails is crucial to protect yourself and your organization. Here’s a straightforward guide on how to spot suspicious emails and ensure your safety online.Email Header Ana
TikTok Compliance Data Your New BFF
Haven’t heard of TikTok? Then you might have been living under a rock (or maybe just enjoying some serious digital detox!). TikTok is one of the world’s most popular social media platforms, where users share short-form, often viral videos, featuring dance challenges, funny skits, DIY tutorials, prod
OSINT Tools And Techniques for Digital Forensics Nerds
Written by: Stephanie HonoreIntroduction As a professional software engineer with a passion for digital forensics, I often find myself drawn to unraveling the complexities of cyber threats in my spare time. With a background in building eDiscovery software and some education in digital forensics,
Phishing Attacks via Social Media
When it comes to cybersecurity, it’s common to underestimate the risk of cyber threats infiltrating your home. Yet, the reality is that with children who may not be fully aware of cyber safety measures, it’s easy for threats to creep in. Recently, one of my children encountered a concerning scenario
Making an Investigations Sock Puppet
Transcript Hello and welcome to the next edition of, the Forensic Impact blog. I’m Amber Schroader. I have been off the video blog for a hot minute because I have broken my ankle, as you can see by my scooter. This is the best background I can get going right now. So, this week I
Empowering Small Businesses: The Significance of Data Governance
Guest Blog Post In today’s digitally driven world, data is the lifeblood of businesses, regardless of their size. Small businesses, in particular, stand to gain significantly from harnessing the power of data. This article from Paraben Corporation delves into the fundamentals of data governance and
Strengthening Your Career In Digital Investigations
Transcript Hi there, and welcome to another installment of forensic impact. I’m Amber Schroader, and this week I am sharing with you information about strengthening your career in digital investigations. This was a topic conversation that I had with one of the blog subscribers, and they said it woul
2023 Review 2024 Predictions
Transcript Welcome to the first blog post of 2024 of Forensic impact. I’m Amber Schroader. I’m the one who maintains this blog. It’s one of those that I have gone up and down about getting stuff written because there’s always piles of research that you can see probably behind me right now. There are
Starting a Business with Little-to-No Startup Capital: Key Strategies for Success
The entrepreneurial journey is filled with challenges, and one of the biggest hurdles can be financial constraints. Many would-be business owners believe they need a hefty sum to launch a venture, but the truth is, you can start small and still go big. The key lies in strategic planning, resourceful
iOS 17 Forensic Impacts
We are in the time of year when our pumpkin spice cravings start crawling to the surface and we see some big releases in the world of mobile firmware. It is a good time to validate and check your tools to see what data you gained and lost with the firmware change. With Apple releasing
How Leadership Can Impact Cybersecurity
Written by: Riley Anne JohnsCybersecurity is a major priority nowadays for business leaders, as no organization is immune to cyber threats. For example, according to Forbes, cyberattackers made roughly $456.8 million in ransomware profits in 2022 alone, as most businesses were unprepared to counter
Different Android Flavors and Forensic Processing
Android, developed by Google, is one of the most popular mobile operating systems worldwide, powering millions of devices. What you might not realize is that there are different tiers of Android OS that are available for millions of devices. We will explore the three primary Android OS types: Oxygen
Small Businesses: Don’t Make These 7 Common Cybersecurity Mistakes
Guest Blog Post: Lance Cody-ValdezHackers are going after SMBs with a vengeance, 43 percent of all cyberattacks are directed toward these smaller companies, according to a Hacked report. SMBs make for “soft” targets, as many don’t have basic cybersecurity safeguards in place and are uninformed whe
Why is Triage a good step in Digital Forensics?
Many people discount the value of triage. Investigators try to obtain all the data at once, which can be costly and unproductive. With the data gap gone between mobile and computer-related data, you can analyze terabytes now without breaking a sweat. Triage and digital forensics are two related but
Fall is full of new data in iOS 16 messages
With each fall we see changes in the smartphone world with new firmware updates that bring extra spice to the pumpkin spice season. This year was not an exception with iOS 16 showing lots of new data that will add to our digital investigations. iOS 16 held a lot of changes in general that were
Investigating Current and Future Vulnerabilities of Electric Vehicle Charging Networks
Blog by: Cameron Cisneros, Zachary Wilson, Karla Soler and Ian Yates Research by: Felix Murray, Cameron Cisneros, Zachary Wilson, Karla Soler, Ian Yates, Unny Menon, Richard D’souza Sponsored by: When we began our research into vulnerabilities of electrical vehicle (EV) charging networks, we had no
23 Years of Innovations from Small Business
Starting 24 years of being a small business in the digital forensic investigations space is a rare activity. With many transitions happening with the different technology providers being sold, going public, or just disappearing it is rare to experience this many years standing strong. So, on this an
Cornerstones of a good digital forensics’ lab
Guest Blogger Hilary Rodela, Lead Digital Content Writer for Taction USA Collecting and extracting evidence is half the battle when it comes to seizing evidence and processing a crime scene. When you don’t have the right supplies or resources it can impede your investigation or even ruin the chain
Five Cybersecurity Fundamentals for Small Businesses
Whether you plan to launch your first company soon or you are a well-established business owner, cybersecurity should mean a great deal to you. Criminals love to target small companies because they are less likely to have stringent security systems and protocols in place. Even if you are operating w
How to get started in the field of digital forensics
When you think of different career paths in the field of cyber you might not always notice the field of digital forensics. However, if you have a passion for all things digital and keen attention to detail this field could be the perfect place for you where a job is not to work, but something
Expectations of Facebook Data
As social media continues to rise so does the power of Facebook. If you are not on it personally you are for your business or to connect with people on a hobby. That being part of the Meta universe has become as essential as getting a driver’s license. So, what does this mean in the
EMI Shielding & Why You Need It
The topic of Physics may not be the first thing that comes to mind when you think of digital forensics, but it does play a key role in the preservation of your digital evidence. Not every organization is lucky enough to have their lab so isolated that they get no issues with signals that could
Due Diligence of Tool Selection
In the season of shopping, many of you might be considering shopping for new tools for your labs. I stepped back to put this together because as I shop for tools for our lab, I don’t judge on the same standard that I do as a tool producer. I, however, always do my due diligence.
Investigating and Capturing Google Data
There are so few people on the planet now that don’t have something to do with Google. With parents selecting Gmail accounts for their kids prior to being born to the proliferation of Google in the classroom the searching giant is everywhere. With this level of distribution also comes the value of t
What is Android ADB with smartphone forensics?
There is a lot of trust put into your digital forensic tools when it comes to processing data. Many times, the “magic” of the tool remains someone unknown to the end-user. Each company claims to have a special means to capture the data that is seen in the acquisition. However, what is unsaid by tool
Forensically Imaging Bitlocker
Guest Blogger, Michael Zinn with Micro Systems Management BitLocker is Microsoft’s Full Volume Encryption (FVE) feature in Windows. BitLocker can be used to encrypt operating system volumes, non-Operating System fixed drive volumes, and removable drive volumes. BitLocker relies on one or more Key Pr
The Role of Psychology in Digital Forensics
Written by Riley Anne JohnsAs more people depend on technology for both personal and professional endeavors, digital forensics has never been more important. Digital forensics is a branch of forensic science specifically focused on cybercrime, using computer evidence to support investigations. And i
Waze Data in Smartphones
According to Wikipedia Waze is: Waze is a GPS navigation software app and a subsidiary of Google. It works on smartphones and tablet computers that have GPS support. It provides turn-by-turn navigation information and user-submitted travel times and route details while downloading location-dependent
iOS Backup vs iCloud How can you compare?
When you process an iOS device there are multiple locations that will provide you the data you are looking for. It is important to understand where you can see the differences in those data sources. Depending on your process checklist you might choose a different data source as a primary to compare
TikTok Smartphone Evidence
We have been using the windows of our smartphones for many years to explore the world of social media. One of the most popular areas for exploration over the last few years has been in the newer social media platform of TikTok. TikTok currently has over 2 billion downloads worldwide and is growing e
What Parents Need to Know About Roblox
Shared from a post written by Nicole Gray of Infinity Investigative SolutionsIt’s the number one online entertainment platform for youth under the age of 13, and number two for teens 13-17 so chances are your child and their friends are already on it. Roblox is an online gaming platform where users
The GDPR & The CCPA a Quick Look with a Forensic Twist
With the recent passages of these two key pieces of legislation, many people use the terms of the CCPA and the GDPR together, as if they literally mean the same thing. However, while the two have been crafted and designed to protect Personal Identifiable Information (PII) datasets, the two also have
Data Security Issues With The Remote Workforce
The concept of the Remote Workforce has now become a reality for the long term, going well into 2021, and possibly even beyond. While most Cyber experts were predicting that a near 99% Virtual Workforce was possible in 4-5 years, it came to fruition in just a matter of two months, right when the COV
Securing Smartphones a Digital Forensic Perspective
When you look at the best means to secure your smartphone there are a few key areas to look at. Hardware System Apps Each of these areas can be applied to both iOS (Apple) and Android. When selecting a device, they can be used to determine if you have the best fit or need to
Interview by Safety Detectives
Step into the thoughts of Paraben’s CEO and Founder Amber Schroader. Forensic-Impact Articles
Discord Investigations
Learn what to do to capture data from Discord
Setting up a Digital Forensic Lab Part 2
Now that you have your mind around what it takes to set up the equipment of the lab it is time to start looking at staffing the lab and the management of the flow of the lab. This can be the hardest part because you are dealing with people and what they need on top
Setting Up a Digital Forensic Lab Part 1
For those of you that have had a lab for a while or are just getting started these are some great guidelines to streamline and maximize your time in the lab. From procedure steps to the machine options there are always choices that a lot of times will depend on how much you want to
Jailbreaking iOS Smartphones in 2020
Since October 2007, the process of Jailbreaking has been out in the universe, allowing for deeper access to the mysterious Apple file system. In the beginning, this technique was frowned on in the digital forensics field because of the potential risk to the device evidence. Jailbreaking was also a
AirWatch MDM and E3 Forensic Platform iOS Acquisitions
When dealing with mobile devices and digital forensics one of the most frustrating barriers is a mobile device management (MDM). An MDM allows IT administrators to configure managed mobile devices, install or remove profiles, remove passcodes, and begin a secure erase of the device. MDM usually cons
5G & Digital Forensic Impact
5G is the next generation of high-speed wireless internet and it promises to be a game-changer for connectivity speeds. It will bring faster speeds and lower latency which will enable a wide range of new applications for business and consumers. 5G is designed to be more robust than previous gene
Inside lab vs Outside lab
Many organizations try to balance the value of having an in-house team for digital forensics vs. outsourcing the services. To break it down, we are going to look at it from the perspective of the public sector vs. the private sector.The public sector in the U.S. primarily has in-house teams that do
Basics of Digital Forensics
Your cell phone, laptop, desktop, and every smart device you own hosts a powerhouse of data that can be subject to analysis. When it comes to investigations of crimes, forensic tools make it possible for investigators to retrieve this valuable data from the devices of a crime suspect. However, every
2020 DFIR Predictions & Innovations
In September of 2019, Paraben celebrated its 20th Anniversary, and as such, we are taking the next twelve months to focus on all things that have made Paraben great. With innovation being our first focus, we thought it was a great opportunity to highlight some of the great innovations we made to the
Mobile Forensic Imaging through the years
In 2002 when I did my first interview on mobile forensics, I never could have imagined the field would explode as it has done. I was an innovator, thinking that these small palm devices, Palm PDA at the time, would be the hub of our digital fingerprints. The snippet from the New York Times article be
App Review of Calculator Photo Vault
Often in digital forensics, you end up with odd Apps that you need to review as part of your investigation that your tool does not support. In this quick review, we will look at the App Calculator Photo Vault and the data that can be found from unsupported Apps. Calculator+ Photo Vault v.8.8.0 by F
Court Approved Debate Is my tool valid?
Through the last thirty years of being in digital forensics, the question of what is court approved has come up many different times. This classification is greatly sought after and advertised by many companies that provide technology to the DFIR space. However, there is no magical standard that ex
Mobile Forensics for Me but Not for Thee
Over approximately the last decade, the convergence of smartphone technology, corporate BYOD policies, and the preeminent role of ESI in civil litigation have elevated exponentially the significance of mobile devices as a source of evidence. However, this development arrived with a built-in paradox
Cyber-Forensics 2019 Predictions
As January 2019 comes to an end, it is helpful to look at some of the trends in forensics that will continue to mature as this year unfolds. Twenty nineteen, however, brings two primary areas to the front of discussion for many organizations: Cloud Forensics and Forensics as a Service. With Cloud co
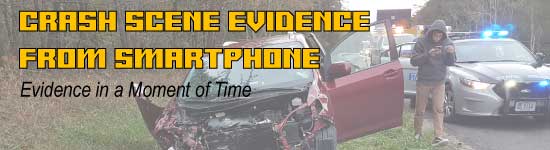
Crash Scene Evidence from Smartphone
Many times, when we do digital forensics, we have a very difficult time finding a starting point for our investigation. It is just a mad dash for data and we are not always able to maintain perspective as we begin weeding through all the information. In a few of our cases we have found that
What is a self-driving car (SDC)?
What is a self-driving car (SDC)?0 Comments A SDC is defined as an unmanned ground vehicle that is capable of sensing its environment and navigating without human input. Other common terms are driverless car, autonomous car, and robotic car. In 2018, self-driving cars will begin to their transition
Extracting email from Zimbra
Extracting email from Zimbra0 Comments Extracting email from Zimbra is not all that challenging. These simple steps show you how. Zimbra is one of the most popular enterprise-class email, calendar, and collaboration solution. It is cloud-based but can also be treated as a standard POP3 mail server.
Digital Forensics of HEIC files from iOS
Guest Blogger: Chief Todd A. Faulkner, Hinsdale Police Department High-Efficiency Image Compression (HEIC) is the new format that applies only to Apple devices that have the A9 processor or more modern. This includes iPhone 6S, 6S Plus, iPad Pro and 2017 iPad 9.7”. Before we discuss how to deal with
Email as digital forensic evidence lives on!
Email is the lifeblood of any organization; as data is transmitted so is the ability to capture it as evidence. With any email processing, there are a simple few rules to follow that allow you to get the maximum amount of data. First, always keep the data in the original structure if possible. Not a
Using Mobile Device Backdoors in Digital Forensics
Guest Blogger: Chief Todd A. Faulkner, Hinsdale Police Department One of the biggest barriers for every investigator is locked devices. We hear countless suggestions that are about tools, but what about adjustments in techniques for the seizure that can work with any tool. For example, with Android
Forensic Collection of Cloud Data
Some people are intimidated when they hear the words ‘cloud’ and ‘digital evidence,’ and immediately start to worry. There is not as much to worry about as one might believe when it comes to actually collect the data. The worry comes into play on the legal restrictions that you might have to access
Mobile Devices: Digital Forensic Data Comparison
Mobile Device Digital Forensics is just coming out of its infancy. The data extracted from a mobile device can also be used to do audits of devices and security checks for vulnerabilities. Using the Mobile Evidence Comparer function in the E3 Platform is one of those features that has multiple func
Tinder, the ticket to dating and data?
After spending time researching Tinder and realizing how happy I was to not be dating, I wondered what electronic nuggets it left behind as one of the top dating apps. As a popular tool for dating, or “getting together,” it becomes a tool of connection for many people and a great way to link Tinder
No articles match your search.